网页
综合
更新时间 2026-11-15 01:10:42
Sphereon Security Architecture Brief - Sphereon
For the modern CISO, “digital identity” is no longer just a checkbox or a standalone category: it is the foundation of a real-world control environment. The primary challenge today isn’t just knowing who someone is, but whether the platform improves specific, high-stakes control points in real-time.
Sphereon’s architecture is built to bridge the gap between “appearance-based” trust—relying on uploaded PDFs, email chains, and manual screenshots—and a truly cryptographically verifiable control path. By moving the focus from documents to data, we turn trust into a scalable operating layer.
In a traditional security model, the “control object” is often a static file, like a scanned certificate or an HR record. Sphereon VDX transforms this business data into verifiable evidence. This ensures that every claim, whether it’s a supplier’s security certification or a contractor’s authorization, is signed at the source and cryptographically bound to the holder. You are no longer managing files; you are managing proofs.
Verification is only as valuable as the action it triggers. Sphereon frames the outcome as a policy-controlled decision, supported by robust workflow and operational tooling. This moves the organization away from ad-hoc, human-intensive checks and toward automated risk treatment.
To eliminate the risk of vendor lock-in and ensure long-term ecosystem health, our technical stack is anchored in recognized global standards. This provides the transparency that security reviewers and regulators expect:
We recognize that every enterprise has a different risk appetite and technical maturity. Sphereon offers three distinct deployment paths to align with your specific operating model:
This is not theoretical software. Sphereon is already executing in multi-stakeholder environments where manual trust is no longer an option. By replacing appearance-based checks with verifiable cryptographic control, this architecture is built specifically for the complexity of the 2026 regulatory landscape and beyond.
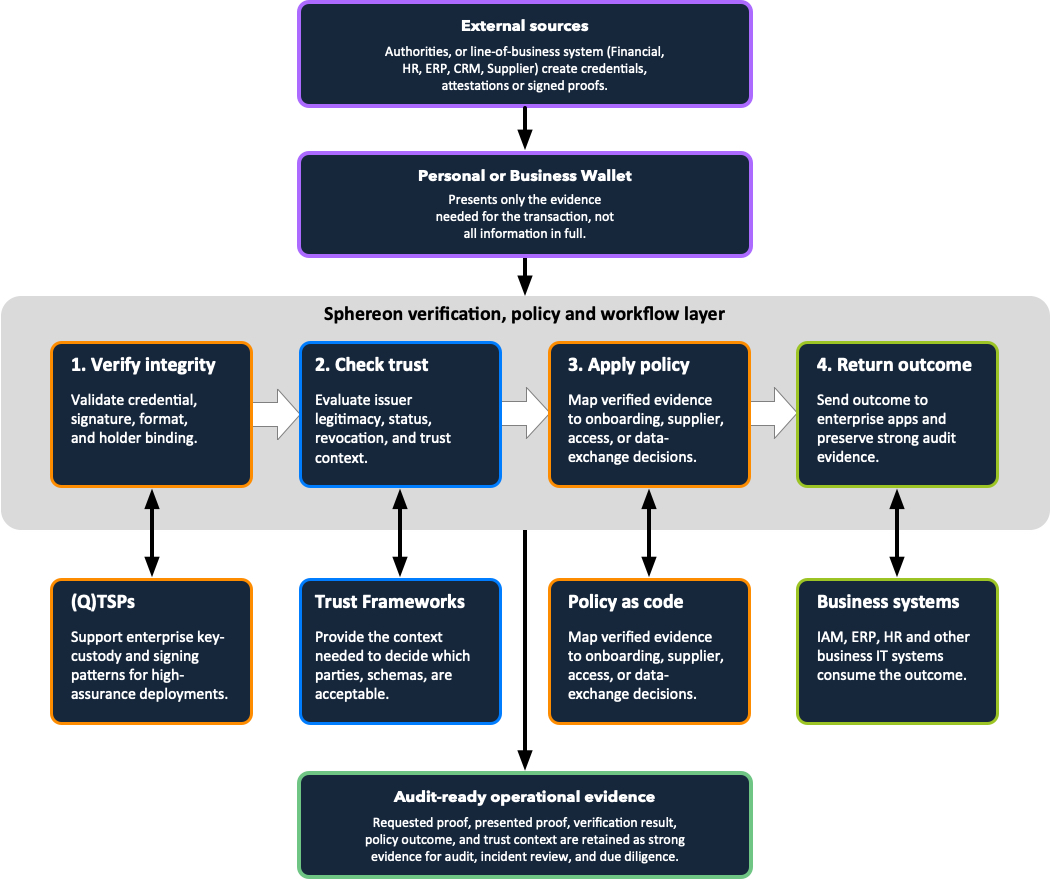
The primary anchor of proof for any security infrastructure is the integrity of its control flow. Sphereon’s architecture is designed to bridge the gap between raw data and business logic by connecting proof creation, trust resolution, and automated verification into a single, unified operating model.
While the control-flow schema traces the high-level movement of data, the following details explain how this architecture functions as a repeatable, standards-based control layer for the enterprise:
As we move through 2026, the European regulatory landscape is shifting from guidance to strict enforcement. With the Dutch Cybersecurity Act (Cbw) entering into force this quarter of 2026, organizations must transition from point-in-time compliance to continuous, verifiable control.
Under the NIS2 directive and the Cbw, the burden of proof rests on the ability to demonstrate that controls are repeatable and supplier-related risks are governed in real-time. Organizations can no longer rely on “best-effort” reconstructions of decisions from PDFs, email chains, and scattered application logs.
The architecture digitizes these high-friction, manual processes into a cryptographically verifiable proof trail. By capturing the requested proof, the trust context, and the policy outcome at the moment of the transaction, the architecture ensures that significant incidents can be investigated and reported within the mandatory 24-hour and 72-hour windows. This moves the organization from point-in-time compliance to a state of continuous, auditable readiness.
The following table demonstrates how the architecture converts high-level regulatory pressure points into specific, auditable technical outcomes.
The architectural value here is not “logging” in the generic SIEM sense. Instead, Sphereon provides a cryptographically verifiable audit trail that captures the entire decision context: exactly what was requested, what was presented, which issuer and trust source were accepted, and which policy logic produced the final decision.
This level of detail is materially stronger under NIS2 scrutiny than any attempt to reconstruct a decision from email chains, static attachments, or scattered application logs after a significant incident has occurred. It transforms your compliance posture from a “best-effort” manual reconstruction into a state of continuous, machine-checkable readiness.
A strategic evaluator must determine whether an architecture exists outside of theory. Sphereon’s maturity is evidenced by its active role in complex, multi-stakeholder environments where manual trust is no longer a viable option. Our software provides the underlying infrastructure for global certification, national tax pilots, and supply chain integrity.
Sphereon provides the trust and control layer for high-stakes operational use cases across diverse, regulated sectors:
To provide a defensible and scalable trust layer, the architecture is organized into a modular stack. This ensures that the core cryptographic protocols remain decoupled from enterprise-specific services and deployment requirements.
Figure 2: The Sphereon technical stack from protocol foundation to application integration.
The layered approach allows an organization to adopt the specific level of control required for their use case, from raw protocol handling to full-scale enterprise orchestration:
A meaningful strength of the Sphereon portfolio is that it does not force a “one-size-fits-all” model. Organizations can align both their engineering capacity and their sovereign hosting requirements with the models that fit their specific risk environment.
Because enterprise key-custody and data sovereignty are critical under NIS2, the platform supports flexible hosting models to ensure you maintain control over your trust infrastructure:
Sphereon is strategically strong because it connects proof creation, trust resolution, policy execution, and evidence retention into a single, cohesi
Sphereon’s architecture is built to bridge the gap between “appearance-based” trust—relying on uploaded PDFs, email chains, and manual screenshots—and a truly cryptographically verifiable control path. By moving the focus from documents to data, we turn trust into a scalable operating layer.
In a traditional security model, the “control object” is often a static file, like a scanned certificate or an HR record. Sphereon VDX transforms this business data into verifiable evidence. This ensures that every claim, whether it’s a supplier’s security certification or a contractor’s authorization, is signed at the source and cryptographically bound to the holder. You are no longer managing files; you are managing proofs.
Verification is only as valuable as the action it triggers. Sphereon frames the outcome as a policy-controlled decision, supported by robust workflow and operational tooling. This moves the organization away from ad-hoc, human-intensive checks and toward automated risk treatment.
To eliminate the risk of vendor lock-in and ensure long-term ecosystem health, our technical stack is anchored in recognized global standards. This provides the transparency that security reviewers and regulators expect:
We recognize that every enterprise has a different risk appetite and technical maturity. Sphereon offers three distinct deployment paths to align with your specific operating model:
This is not theoretical software. Sphereon is already executing in multi-stakeholder environments where manual trust is no longer an option. By replacing appearance-based checks with verifiable cryptographic control, this architecture is built specifically for the complexity of the 2026 regulatory landscape and beyond.
The primary anchor of proof for any security infrastructure is the integrity of its control flow. Sphereon’s architecture is designed to bridge the gap between raw data and business logic by connecting proof creation, trust resolution, and automated verification into a single, unified operating model.
While the control-flow schema traces the high-level movement of data, the following details explain how this architecture functions as a repeatable, standards-based control layer for the enterprise:
As we move through 2026, the European regulatory landscape is shifting from guidance to strict enforcement. With the Dutch Cybersecurity Act (Cbw) entering into force this quarter of 2026, organizations must transition from point-in-time compliance to continuous, verifiable control.
Under the NIS2 directive and the Cbw, the burden of proof rests on the ability to demonstrate that controls are repeatable and supplier-related risks are governed in real-time. Organizations can no longer rely on “best-effort” reconstructions of decisions from PDFs, email chains, and scattered application logs.
The architecture digitizes these high-friction, manual processes into a cryptographically verifiable proof trail. By capturing the requested proof, the trust context, and the policy outcome at the moment of the transaction, the architecture ensures that significant incidents can be investigated and reported within the mandatory 24-hour and 72-hour windows. This moves the organization from point-in-time compliance to a state of continuous, auditable readiness.
The following table demonstrates how the architecture converts high-level regulatory pressure points into specific, auditable technical outcomes.
The architectural value here is not “logging” in the generic SIEM sense. Instead, Sphereon provides a cryptographically verifiable audit trail that captures the entire decision context: exactly what was requested, what was presented, which issuer and trust source were accepted, and which policy logic produced the final decision.
This level of detail is materially stronger under NIS2 scrutiny than any attempt to reconstruct a decision from email chains, static attachments, or scattered application logs after a significant incident has occurred. It transforms your compliance posture from a “best-effort” manual reconstruction into a state of continuous, machine-checkable readiness.
A strategic evaluator must determine whether an architecture exists outside of theory. Sphereon’s maturity is evidenced by its active role in complex, multi-stakeholder environments where manual trust is no longer a viable option. Our software provides the underlying infrastructure for global certification, national tax pilots, and supply chain integrity.
Sphereon provides the trust and control layer for high-stakes operational use cases across diverse, regulated sectors:
To provide a defensible and scalable trust layer, the architecture is organized into a modular stack. This ensures that the core cryptographic protocols remain decoupled from enterprise-specific services and deployment requirements.
Figure 2: The Sphereon technical stack from protocol foundation to application integration.
The layered approach allows an organization to adopt the specific level of control required for their use case, from raw protocol handling to full-scale enterprise orchestration:
A meaningful strength of the Sphereon portfolio is that it does not force a “one-size-fits-all” model. Organizations can align both their engineering capacity and their sovereign hosting requirements with the models that fit their specific risk environment.
Because enterprise key-custody and data sovereignty are critical under NIS2, the platform supports flexible hosting models to ensure you maintain control over your trust infrastructure:
Sphereon is strategically strong because it connects proof creation, trust resolution, policy execution, and evidence retention into a single, cohesi
本页为82搜索生成的网页快照,内容来自站内索引;演示数据的原文链接仅作示例。